.png)
Sep 7, 2026Blog
UNEY Goes Green: Taking Practical Steps Towards a More Sustainable Workplace
Discover how UNEY is taking practical steps towards a greener workplace through waste segregation, sustainability, and responsible everyday practices.

The global cybersecurity workforce shortage has reached 4.8 million unfilled positions, creating unprecedented opportunities for career growth.
Whether you’re starting as a junior SOC analyst or transitioning mid-career into cybersecurity, understanding the complete career roadmap—from entry-level roles earning $65K to executive CISOs commanding $300K+—is essential for planning your professional journey. This guide provides the skills, certifications, and salary benchmarks you need at every stage, backed by the NIST NICE Framework and current market data.
At UNEY, we believe cybersecurity careers should be accessible to everyone with the right guidance and practical skills. This comprehensive roadmap breaks down complex career progression into simple, actionable steps that anyone can follow.
What is a Cybersecurity Career Path?
A cybersecurity career path is a structured progression through increasingly specialized and senior roles within the information security field. Unlike traditional IT careers, cybersecurity offers multiple specialization tracks—from technical hands-on roles like penetration testing to strategic positions like security architecture and executive leadership.
According to the NIST NICE Cybersecurity Workforce Framework, cybersecurity work is organized into seven core categories: Securely Provision, Operate and Maintain, Oversee and Govern, Protect and Defend, Analyze, Collect and Operate, and Investigate. Each category contains multiple role pathways that professionals can pursue based on their interests and strengths.
The U.S. Bureau of Labor Statistics reports that information security analyst employment will grow 29% from 2024 to 2034—much faster than the average for all occupations. This explosive growth reflects the critical importance organizations place on protecting digital assets and the persistent talent shortage across all experience levels.
What makes cybersecurity career paths unique is their flexibility. Professionals can:
The field rewards both technical depth and business acumen, making it accessible to professionals with diverse backgrounds including IT support, network administration, software development, and even non-technical fields like finance or law enforcement.
Why Your Cybersecurity Career Path Matters Now More Than Ever
The cybersecurity talent gap represents both a challenge and an extraordinary opportunity. Organizations worldwide are actively recruiting at all experience levels, creating competitive salaries, rapid advancement opportunities, and job security that few other fields can match.
1. Unprecedented Demand Across All Levels
The cybersecurity workforce shortage isn’t limited to senior positions. According to CyberSeek’s Career Pathway analysis, demand exists at every career stage:
This demand translates to competitive starting salaries even for entry-level positions, with junior SOC analysts earning between $65,000-$85,000 annually in most U.S. markets.
2. Regional Growth and Global Opportunities
Cybersecurity career opportunities are expanding beyond traditional tech hubs. The Middle East, particularly the UAE, has seen cybersecurity job postings increase by 47% year-over-year as digital transformation initiatives accelerate. Similarly, Southeast Asian markets like Vietnam are investing heavily in cybersecurity infrastructure, creating new opportunities for professionals at all levels.
These regional markets often offer:
3. Multiple Entry Points for Career Changers
Unlike many specialized fields, cybersecurity welcomes career changers. A LinkedIn Talent Trends report found that 43% of current cybersecurity professionals came from non-security backgrounds including:
This accessibility, combined with numerous certification pathways that don’t require degrees, makes cybersecurity an attractive option for mid-career professionals seeking better compensation and job security.
The Cybersecurity Career Framework: Understanding Your Options
Before diving into specific roles, it’s essential to understand how cybersecurity careers are structured. The NIST NICE Framework organizes cybersecurity work into seven broad categories, each containing multiple specialized roles.
Security Operations (Protect and Defend)
These roles focus on day-to-day security monitoring, incident response, and threat mitigation:
Engineering and Architecture (Securely Provision)
Technical specialists who design and implement security solutions:
Offensive Security (Analyze)
Professionals who identify vulnerabilities through simulated attacks:
Governance and Management (Oversee and Govern)
Leaders who develop strategy, manage teams, and ensure compliance:
Specialized Tracks
Niche areas requiring specific expertise:
Understanding these categories helps you identify which path aligns with your interests, current skills, and career goals. Most professionals start in Security Operations before specializing or moving into management tracks.
Complete Cybersecurity Career Roadmap: Entry to Executive
Level 1: Entry-Level Positions (0-2 Years Experience)
Typical Roles: Junior SOC Analyst, IT Security Coordinator, Security Support Technician
Salary Range: $65,000 - $85,000 annually
Entry-level cybersecurity roles focus on monitoring, detection, and basic incident triage. You’ll work within established procedures under senior guidance, learning to identify threats and respond according to documented playbooks.
Core Responsibilities:
Required Skills:
Recommended Certifications:
Career Tip: Focus on building strong foundational knowledge across networking, systems, and security concepts. Entry-level roles provide invaluable exposure to real-world threats and incident handling processes that inform all future career decisions.
Level 2: Intermediate Positions (2-5 Years Experience)
Typical Roles: SOC Analyst (Tier 2), Security Analyst, Junior Security Engineer
Salary Range: $85,000 - $120,000 annually
At the intermediate level, you’ll take ownership of more complex investigations, perform deeper analysis, and begin specializing in specific security domains. Your recommendations start influencing security tool selection and process improvements.
Core Responsibilities:
Required Skills:
Recommended Certifications:
Specialization Paths:
At this stage, many professionals begin specializing:
Level 3: Advanced Positions (5-8 Years Experience)
Typical Roles: Senior Security Analyst, Security Engineer, Penetration Tester, Incident Response Manager
Salary Range: $120,000 - $160,000 annually
Advanced-level professionals own significant security domains, lead complex projects, and make architectural decisions. Your expertise shapes organizational security strategy and you regularly interface with business leadership.
Core Responsibilities:
Required Skills:
Recommended Certifications:
Technical Depth vs. Management Track:
This level represents a critical decision point. You can continue building deep technical expertise (Staff Engineer, Principal Security Engineer) or transition to management (Security Manager, Team Lead). Both paths lead to senior compensation but require different skill development.
Level 4: Expert/Leadership Positions (8-12 Years Experience)
Typical Roles: Security Architect, Cybersecurity Manager, Senior Security Engineer, Director of Security Operations
Salary Range: $160,000 - $220,000 annually
Expert-level positions combine deep technical or managerial expertise with strategic thinking. You’ll own entire security domains, lead multiple teams, and directly influence organizational risk posture.
Core Responsibilities:
Required Skills:
Recommended Certifications:
Key Differentiator: At this level, business acumen becomes as important as technical skill. Understanding organizational strategy, financial planning, and executive communication separates good managers from great security leaders.
Level 5: Executive Leadership (12+ Years Experience)
Typical Roles: Chief Information Security Officer (CISO), VP of Security, Director of Cybersecurity, Security Practice Leader
Salary Range: $220,000 - $500,000+ annually (plus equity, bonuses)
Executive security leaders set organizational cybersecurity vision, manage enterprise-wide risk, and serve as the voice of security to boards, executives, and external stakeholders. CISOs bridge technology and business, translating technical risk into business impact.
Core Responsibilities:
Required Skills:
Recommended Credentials:
Path to CISO:
Most CISOs follow one of three paths:
The CISO role requires balancing technical knowledge, business strategy, and leadership capabilities—making it one of the most challenging yet rewarding positions in technology.
Cybersecurity Career Progression: Comparison at a Glance
Understanding how different factors compare across career levels helps you plan your progression strategically.
Career Level | Avg. Salary (US) | Key Focus | Primary Skills | Time to Next Level | Certification Priority |
Entry (0-2 yrs) | $65K - $85K | Monitoring & Basic Response | Networking, SIEM Tools, Documentation | 18-24 months | Security+, Network+ |
Intermediate (2-5 yrs) | $85K - $120K | Investigation & Analysis | Scripting, Malware Analysis, Cloud | 2-3 years | CEH, CySA+, Cloud Certs |
Advanced (5-8 yrs) | $120K - $160K | Specialization & Leadership | Architecture, Advanced Tools, Mentorship | 3-4 years | CISSP, OSCP, CCSP |
Expert (8-12 yrs) | $160K - $220K | Strategy & Team Management | Enterprise Architecture, Risk, Budget | 3-5 years | CISM, GSLC, SABSA |
Executive (12+ yrs) | $220K - $500K+ | Vision & Business Alignment | Executive Communication, Board Governance | Continuous Growth | MBA, Board Certifications |
Key Insights:
How to Advance Your Cybersecurity Career: A Practical 7-Step Framework
Moving through the cybersecurity career ladder requires intentional planning beyond simply gaining experience. Here’s our approach to strategic career advancement that we see work consistently.
Step 1: Master Current Role Fundamentals First
Before pursuing promotion, ensure you’ve truly mastered your current responsibilities. This means:
Many professionals jump to new certifications without fully mastering current roles, limiting their advancement potential.
Step 2: Identify Your Specialization or Management Track
Around the 3-5 year mark, actively choose your direction:
Your personality, strengths, and interests should drive this decision, not just compensation (both tracks can lead to $200K+ roles).
Step 3: Build T-Shaped Expertise
Develop a “T-shaped” skill profile:
For example, an SOC analyst might have broad knowledge of networks, cloud, and applications (horizontal), with deep expertise in SIEM engineering and threat hunting (vertical).
Step 4: Obtain Strategic Certifications
Plan certifications based on career stage and goals:
Certifications signal competency to employers but don’t replace hands-on experience. Balance certification study with practical skill application.
Step 5: Build a Public Professional Presence
Visibility accelerates advancement:
This visibility positions you as a thought leader and makes you attractive to hiring managers and executive teams.
Step 6: Navigate Internal Politics and Build Relationships
Technical skill alone doesn’t guarantee advancement. Political savvy matters:
Many technically brilliant professionals stall because they neglect relationship-building.
Step 7: Know When to Leave (and When to Stay)
Sometimes advancement requires changing organizations:
Job changes typically yield 15-25% salary increases versus 3-5% annual raises. However, frequent job-hopping (less than 18 months per role) can signal instability to future employers.
Challenges in Cybersecurity Career Progression (and How to Overcome Them)
Every career path has obstacles. Understanding common challenges helps you navigate them proactively.
Challenge 1: Breaking Into Entry-Level Roles Without Experience
The “need experience to get experience” paradox affects cybersecurity newcomers. Organizations want proven skills, but entry-level candidates lack professional security experience.
Solutions:
According to Cybersecurity Guide’s research, 67% of entry-level positions consider equivalent experience and certifications in lieu of formal degrees.
Challenge 2: Overcoming Mid-Career Plateaus
Many professionals hit plateaus around the 5-8 year mark, struggling to advance beyond intermediate roles despite strong technical skills.
Solutions:
The transition from “doing security” to “leading security” requires intentional skill development beyond technical depth.
Challenge 3: Balancing Specialization vs. Breadth
Too much specialization limits mobility; too much breadth prevents deep expertise needed for senior roles.
Solutions:
According to CyberSeek data, professionals with cloud security skills plus one other specialization have 43% more open positions available than single-specialty professionals.
The UNEY Approach to Cybersecurity Career Development
At UNEY, we believe cybersecurity careers should be built on practical skills, continuous learning, and accessible security practices. Our approach to career development reflects our core values: simplicity, accessibility, trust, and scalability.
Security Skills Should Be Practical and Accessible
Traditional cybersecurity career advice often emphasizes expensive degrees, multiple certifications, and years of experience before entry. We disagree. While education and certifications have value, they’re not absolute requirements for starting and advancing in cybersecurity.
We’ve seen successful cybersecurity professionals emerge from:
Our recommendation: Focus first on building demonstrable practical skills through hands-on labs, home projects, and open-source contributions. Certifications validate knowledge but don’t replace applied capability.
Career Progression Should Enable Business Outcomes
Too often, cybersecurity career paths focus purely on defensive capabilities without connecting to business impact. This mindset limits advancement potential, especially for senior and executive roles.
At every career stage, we encourage professionals to:
This business-aligned approach accelerates advancement into leadership roles where strategic thinking matters as much as technical expertise.
Security Careers Should Scale With Changing Threats
The cybersecurity landscape evolves rapidly. Career paths built on static knowledge become obsolete quickly. Successful long-term careers require adaptability and continuous learning.
UNEY’s platform embodies this principle by making enterprise-grade security accessible to organizations at all stages. Similarly, your career should scale through:
The most successful cybersecurity careers aren’t built on perfect initial planning, but on consistent growth and adaptation to changing conditions.
FAQ: People Also Ask About Cybersecurity Career Paths
What degree do I need for a cybersecurity career?
While many employers prefer bachelor’s degrees in computer science, information security, or related fields, they’re not absolute requirements. According to the Bureau of Labor Statistics, many cybersecurity professionals enter the field through IT certifications, bootcamps, and self-study combined with practical experience. Focus on building demonstrable skills through certifications like Security+, hands-on labs, and documented projects.
How long does it take to become a cybersecurity analyst?
Entry-level security analyst positions typically require 0-2 years of relevant experience, which can include IT support, helpdesk, or network administration roles. With focused preparation including Security+ certification and practical labs, motivated individuals can transition into junior analyst roles within 6-12 months. Advancing to senior analyst levels takes an additional 3-5 years of experience.
Can I transition into cybersecurity from a non-technical background?
Yes, many successful cybersecurity professionals come from non-technical backgrounds. Skills from law enforcement (investigation), finance (risk assessment), project management (organization), and even teaching (communication) translate well into security roles. Start by building technical foundations through certifications like Security+ or Google Cybersecurity Certificate, then pursue entry-level positions that leverage your existing strengths combined with new technical skills.
What certifications should I get first for a cybersecurity career?
For complete beginners, start with CompTIA Security+ ($404), which covers foundational security concepts and is widely recognized. If you lack networking knowledge, CompTIA Network+ provides essential background. ISC²’s Certified in Cybersecurity (CC) offers a free entry-level option. After establishing fundamentals, pursue specialization certifications like CEH (ethical hacking), CySA+ (analyst skills), or cloud certifications based on your career direction.
How does UNEY help with cybersecurity career development?
UNEY provides practical, scalable security solutions that help professionals at all career stages understand how enterprise security operates in real-world environments. Whether you’re learning security fundamentals or advancing to senior roles, understanding how accessible security platforms enable business outcomes strengthens your practical knowledge and strategic thinking—critical skills at every career level.
Conclusion
The cybersecurity career landscape offers unprecedented opportunities for professionals at every stage—from entry-level analysts to executive CISOs. With 4.8 million unfilled positions globally, strong salary growth (29% employment growth through 2034), and multiple specialization tracks, cybersecurity provides both job security and meaningful work protecting organizations from evolving threats.
Success requires more than technical skill alone. The most successful careers combine technical depth, business acumen, continuous learning, and strategic relationship-building. Whether you’re just starting, mid-career, or advancing to executive leadership, focus on practical skills, intentional specialization choices, and clear communication of your value.
The future of cybersecurity belongs to adaptable professionals who can translate complex technical concepts into business outcomes while continuously evolving with emerging threats and technologies.
Ready to take the next step in your cybersecurity career? Explore how UNEY makes enterprise security accessible and practical, helping organizations build security capabilities that scale—and helping professionals understand how effective security enables business success.
Discover how UNEY is taking practical steps towards a greener workplace through waste segregation, sustainability, and responsible everyday practices.
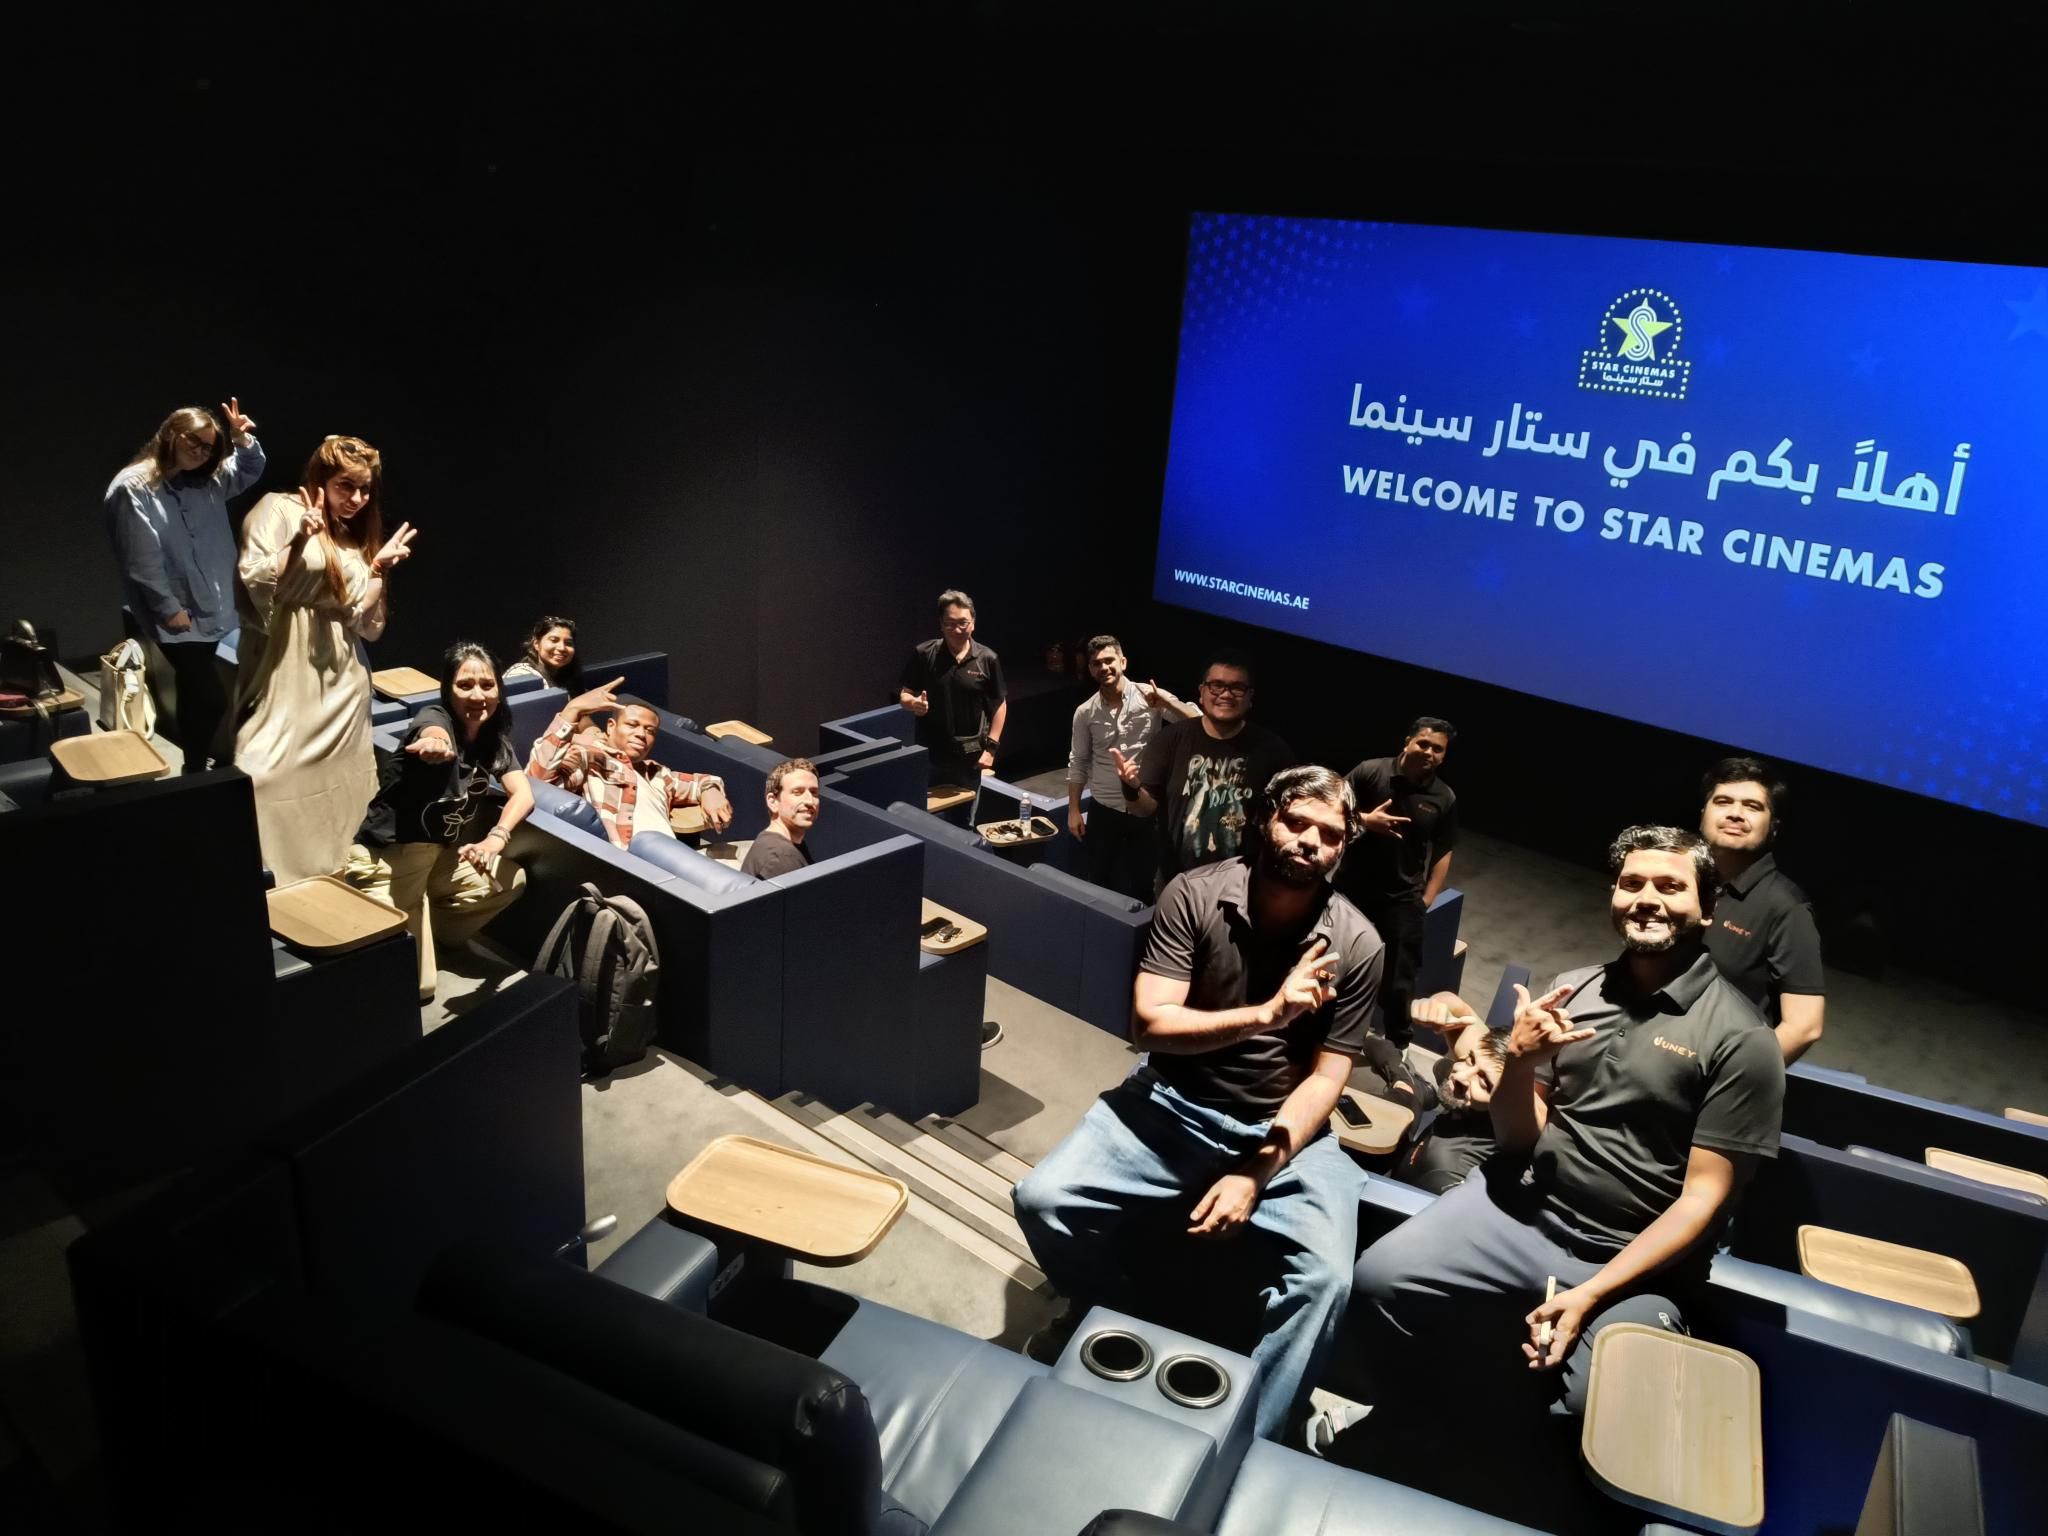
Discover how UNEY’s SkyTrack and ShieldNet 360 were showcased on the big screen, highlighting our commitment to innovation, digital transformation, and expanding the reach of our technology.
.jpeg)
UNEY introduces the ONE TEAM Recreation Lounge, a dedicated space promoting employee wellbeing, connection, collaboration, and a stronger workplace experience.

Reach out to discuss how UNEY can help secure your digital world.
